CyberNEMO Tools: First Validation Results in the Supply Chain / Smart Agriculture Pilot

CyberNEMO has started initial validation of its integrated tools within the pilots and specifically the Supply Chain / Smart Agriculture pilot, led by ENTERSOFTONE and technically supported by SYNELIXIS. The validation largely covers the end-to-end cybersecurity risk management process, i.e. from scope establishment to detection, decision support and countermeasure enforcement, across the computing continuum composed by:

-The dedicated pilot cluster hosted in a commercial cloud provider

-The NEMO and CyberNEMO clusters hosted by OneLab facility of Sorbonne University.

In terms of tools, Monikube extracts topology discovery, asset reading, and vulnerability identificationand assessment. AI-FWaaS detects cybersecurity incidents while the IPDM DSS correlates threat intelligence with asset risk profiles to generate response recommendations. The CyberNEMO Policy Manager (CNPM) enforces network policies as countermeasures across the infrastructure.

Services run across the pilot’s Kubernetes cluster and the shared OneLab infrastructure, which hosts both CyberNEMO and NEMO project clusters while the multi-site architecture allows for local and centralised deployment modes.

Read More

CyberNEMO contributes to AIOTI – Mutual Reinforcement

CyberNEMO has submitted its contribution to the AIOTI report on the IoT and Edge Computing EU-funded Projects Landscape (Release 5.0).

CyberNEMO brings to AIOTI a timely contribution at the frontier of the IoT and edge security agenda. Specifically, CyberNEMO contribution referred to a set of research challenges confronted by the project including:

  • Zero Trust and dynamic identity management across heterogeneous continuum environments.
  • AI-powered runtime threat detection and self-healing architectures at the edge.
  • Privacy-preserving federated learning for secure AI model lifecycle management.
  • Kubernetes and container security at scale in multi-cluster deployments.
  • Federated and decentralised security policy management.
  • Cross-domain Cyber Threat Intelligence sharing with IDMEFv2 and STIX.
  • Secure lifecycle and update management for distributed IoT/edge services.
  • Explainable, human-centric decision support for security operators.

Through AIOTI, the project is acquiring access to a high-impact dissemination channel reaching the European research, standardisation, and policy communities and positioning the project within the broader IoT and edge computing ecosystem.

Read More

Privacy Protection Enforcement (PPE)

The Privacy Protection Enforcement (PPE) component has been designed and developed by CyberSocial Lab  within the CyberNEMO project and publicly accessible on the Eclipse Research Labs repository,
Our tool acts as a privacy-aware authorization and enforcement mechanism supporting secure data sharing across the computing continuum. Operating in conjunction with the Computing Continuum Access Security Broker (CASB), the PPE is responsible for ensuring that access to personal and sensitive data is granted only when the applicable processing policies and user consents are satisfied.

The architecture of the PPE has been designed to support secure and trustworthy data exchanges across cloud, edge, and IoT environments, while promoting data sovereignty, privacy preservation, and regulatory compliance. By combining policy-based access control mechanisms with consent management capabilities, the component enables organizations to maintain control over how sensitive data is accessed and processed across distributed infrastructures.

PPE provides a structured framework for defining and enforcing privacy and data access requirements. Indicative controls and verification mechanisms supported by the component include:

  • Validation of consent records before access to protected data is granted.
  • Enforcement of data processing policies applicable to data consumers.
  • Verification of consent validity and policy applicability during access requests.
  • Auditing and traceability of authorization and access control decisions.
  • Verification of cryptographic proofs associated with policies and consents.

The PPE has been designed in alignment with the principles of the General Data Protection Regulation (GDPR), supporting key requirements such as lawful processing, explicit consent management, accountability, transparency. It contributes to ensuring that sensitive data is accessed only when valid consent and an applicable processing policy exist.

Furthermore, the use of cryptographic proofs and immutable audit trails strengthens accountability by providing verifiable evidence of consent and authorization decisions throughout the data lifecycle. The adoption of blockchain-based evidence storage, rather than storing personal data directly on-chain, supports privacy-preserving processing practices while facilitating regulatory compliance across distributed cloud, edge, and IoT environments.

PPE integrates with the broader CyberNEMO security ecosystem through the CASB. When a data consumer requests access to protected data, the component evaluates the corresponding policies and consents before authorizing the request. Authorization outcomes can be propagated to other platform components, enabling coordinated security, governance, and compliance operations across the CyberNEMO architecture.

The component is currently under development and will contribute to the implementation of secure, privacy-preserving data sharing services compliant with applicable regulatory requirements across the CyberNEMO computing continuum. In line with the CyberNEMO open-source strategy, the PPE is released under the Apache License 2.0. 
Read More

CyberNEMO at the EE-ISAC / JE-ISAC / E-ISAC Joint Webinar

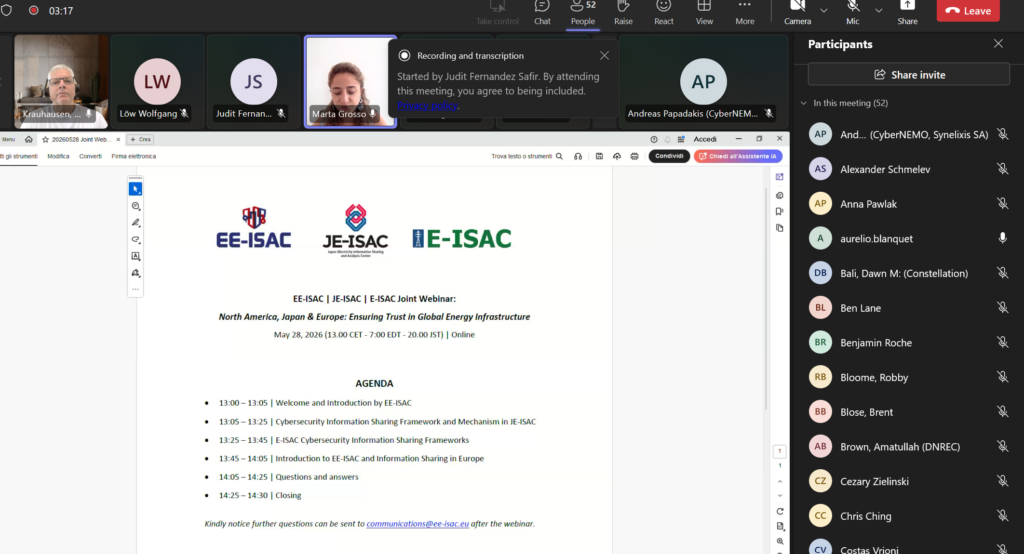
On May 28, CyberNEMO partners (Synelixis, Maggioli and Netcompany) attended and participated in the joint webinar “North America, Japan and Europe: Ensuring Trust in Global Energy Infrastructure”, organised by the European Energy Information Sharing and Analysis Centre (EE-ISAC), the Japanese ISAC (JE-ISAC), and the North American E-ISAC.

Aspects related to trust, threat intelligence sharing, and operational coordination were discussed. The webinar covered the current state and future direction of Cyber Threat Intelligence (CTI) sharing among ISACs and their members. The necessity for anonymisation, the adoption of TLP classification levels, the automation based on APIs and the role of STIX for structured threat information have been presented and discussed. The increasing presence of AI-driven threat campaigns and AI tools for in-depth threat analysis were also pointed out, while a challenging point has been the one-way incident reporting practices and the still-evolving automation of information flows between operators, C-SIRTs, ENISA, and ISACs.

CyberNEMO project coordinator discussed with EE-ISAC representative Thomas Krauhausen (https://www.ee-isac.eu/who-we-are/) on the information flow from an energy operator, through C-SIRT, ENISA, and ISAC structures, to other EU operators and the role of STIX to enable automation that accelerates NIS2-mandated steps while enriching the semantic quality of shared data. The discussion confirmed that STIX-based automation remains a priority direction.

The presentations and discussions validated pillars of the SAAM platform currently under development within CyberNEMO. The challenges reported by ISAC practitioners, fragmented communication flows, limited automation are aligned with SAAM objectives.

Read More

DNV Cybersecurity Research Day 2026: Continuous Risk Management and Certification of Critical Systems – a Challenge in Cybersecurity

Cybersecurity assurance cannot be achieved at isolated points in time. Technologies, vulnerabilities, and threats evolve constantly, and system owners need continuous insight into their security posture. Emerging regulations, including the EU Cyber Resilience Act, the AI Act, and NIS2, are further raising the bar for both providers and operators of digital systems.

DNV Cybersecurity Research Day 2026: Continuous Risk Management and Certification of Critical Systems – a Challenge in Cybersecurity is dedicated to cybersecurity assurance through continuous risk management and certification of critical systems. CyberNEMO project will present research results, covering methods and tools currently in development

The event is expected to bring together industry leaders, CISOs, researchers, and regulatory authorities to share the latest knowledge and discuss the road ahead. Framing the regulatory context and exploration of what organisations need to succeed with cybersecurity assurance in practice are also included in the agenda.

Read More

CyberNEMO Releases the Network Policy Manager (CNPM)

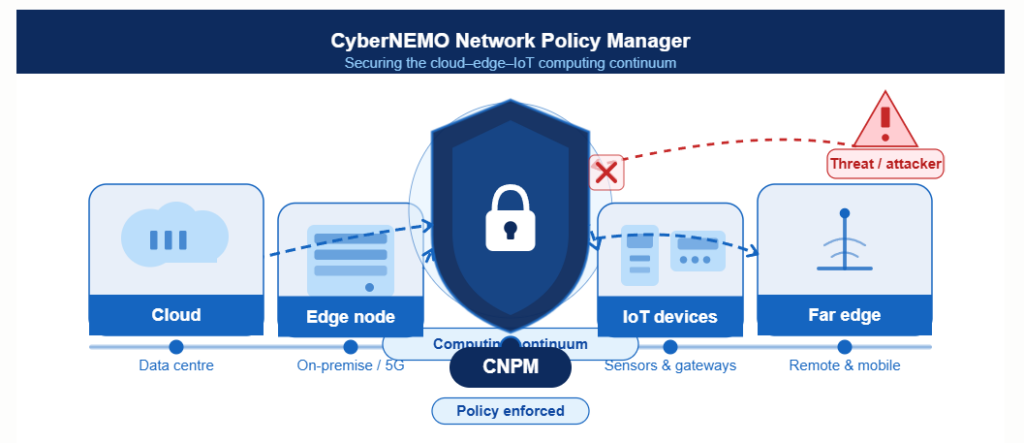
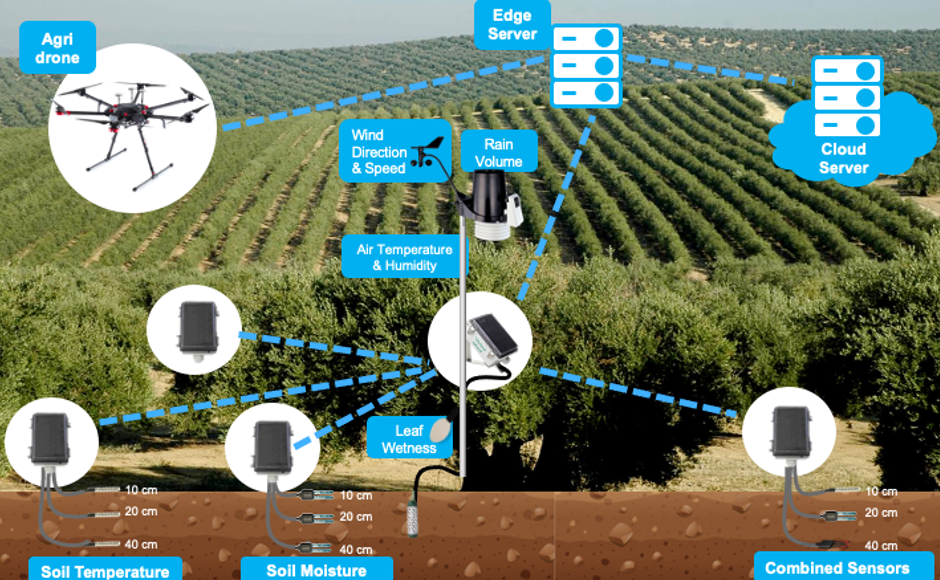
The alpha version of the CyberNEMO Network Policy Manager (CNPM), a policy enforcement component of the CyberNEMO cybersecurity platform, developed by Synelixis SA and publicly accessible on the Eclipse Research Labs repository, undergone under initial testing and validation in the Smart Agriculture / Supply Chain pilot.

CNPM is designed for the cloud–edge–IoT continuum as it operates natively within Kubernetes, the de facto orchestration standard for containerised applications. It is based on Cilium networking layer that enables fine-grained, identity-aware security controls across distributed clusters. Each cluster in a CyberNEMO deployment runs its own CNPM instance, ensuring that policy management remains local, responsive, and aligned with the specific security posture of that environment.

CNPM provides the operators a structured, template-driven workflow for defining and enforcing network security policies. Indicative policies that CNPM can create and enforce include:

  • Deny-all ingress rules that block all inbound traffic to a namespace by default, enforcing an explicit allowlist model.
  • Least-privilege access controls that permit only the minimum necessary communication between services.
  • Source-based filtering, restricting traffic to specific IP ranges or trusted origins.
  • Port-level controls, limiting exposure to only the protocols and ports a service legitimately requires.

Policies can be generated from reusable templates, validated before deployment, and pushed directly to the cluster, reducing the risk of misconfiguration and ensuring consistency across environments.

CNPM integrates with the CyberNEMO event bus, receiving mitigation instructions from upstream platform components such as the Cloud Access Security Broker (CASB) and the Intrusion Prevention Detection and Mitigation Decision Support System (IPDM-DSS), closing the loop between threat detection and network-level response.

The module is released under the Apache License 2.0.
Read More

CyberNEMO attends the CEI-Sphere and LSP O-CEI and COP-Pilot Webinar on Privacy-Enhancing Technologies

CyberNEMO partners (Synelixis and Maggioli) attended the webinar on Privacy-Enhancing Technologies for Information Security in Edge-Cloud Applications, organized by CEI-Sphere and Large Scale Pilots O-CEI and COP-Pilot.

The webinar explored the growing challenge of securely sharing and processing data across distributed environments, from industrial platforms to smart infrastructures, where large numbers of devices, man-in-the-middle threats, and purpose limitation requirements create complex security landscapes. Protecting sensitive data today goes well beyond personal data as business data sovereignty is equally at stake.

Presentations from Fraunhofer ISST and insights from the O-CEI and COP-PILOT Large-Scale Pilots highlighted how technologies such as Federated Machine Learning (FML), Trusted Execution Environments, Homomorphic Encryption, and Zero-Knowledge Proofs can be embedded directly into system design. The “black sheep problem” in FML, identifying and mitigating malicious or corrupted participants in federated learning, is a as a shared concern directly relevant to CyberNEMO’s work on ZT-FML.

CyberNEMO identified synergies in two areas a) the Zero-Trust Federated Machine Learning (ZT-FML) and b) the use of LLMs and MCP-based architectures for privacy-aware decision support functionality.

Read More

CyberNEMO Meets IDMEFv2: Employing, Supporting and Contributing to Incident the Detection Standard

CyberNEMO project, represented by the Coordinator Synelixis and partner Maggioli, met Gilles Lehmann, lead of the IDMEFv2 Task Force, on 30 April 2026, for a focused exchange on IDMEFv2 standardisation developments and its usage in the context of the project.

In the context of IDMEFv2 standardisation effort, draft v08 has been published in April 2026 and the IETF meeting scheduled for July 2026, where the standard is seeking to advance towards an Experimental RFC status.

CyberNEMO is as one of the projects employing IDMEFv2 (link). Specifically, IDMEFv2 is used in the communication backbone between heterogeneous security detectors and the Decision Support System. By adopting a standardised, JSON-based incident description format, the project enables diverse sensors to feed alerts into a unified pipeline. The usage of IDMEFv2 across the computing continuum allows for suggestions to the standard on behalf of the CyberNEMO consortium, an effort led by partner Maggioli who provides one of the main detector AI-based Firewall as a Service.

Both sides concluded that this partnership is going to level up the standard and bring some serious momentum to the project, while this contribution is foreseen to have a significant impact on the domain and will play a pivotal role in future developments.

Read More

EC Cybersecurity cluster 3rd meeting

The CyberNEMO project was present in the 3rd meeting of the European Cybersecurity Cluster along with INTACT, CASTOR, and MIRANDA following the meeting that took place on January 16th. This strategic gathering was scheduled to review the projects’ updates since their last meetup and align the shared goals of these leading EU-funded initiatives.

Among the various topics discussed, for CyberNEMO, the presentation of the CyberNEMO Decision Support component was an important milestone. In addition, the projects demonstrated significant interest in co-organizing a workshop in Paris this fall.

The exchange was further enriched by the introduction of three new projects to the cluster: Mediate, CoCyber and GuardAI, expanding the group’s collective expertise in securing the digital landscape.

Read More