From NEMO to CyberNEMO: The Evolution of Network Monitoring

The transition from the NEMO project to CyberNEMO marks a critical evolution in how we approach network visibility within distributed systems. In the original NEMO project, the primary challenge was establishing reliable performance monitoring across diverse infrastructure. Our response, developed by UPM within the networking work package, was White Shark. White Shark was designed as a network probe, focusing on the fundamental socket layer to measure point-to-point communication metrics like latency, throughput, and jitter. This provided a foundational level of observability, allowing operators to understand how the network was performing at any given moment.

However, as we moved into CyberNEMO, the landscape shifted dramatically. The emergence of a true “computing continuum”—spanning Cloud, Edge, and IoT devices—introduced complexity and a expanded attack surface. Simple performance monitoring was no longer sufficient. We realized that the massive stream of high-fidelity network telemetry generated by White Shark was not just performance data; it was a rich, untapped source of security intelligence. The data that previously told us if the network was fast, could now tell us if the network was being compromised.

This realization led to the development of the NADA (Network Anomaly Detection AI) component in CyberNEMO. NADA represents the intelligent brain that sits atop the White Shark sensing layer. Its purpose is to ingest the granular, socket-level data captured by the probe and use advanced machine learning algorithms to identify temporal and contextual anomalies.

The journey from NEMO to CyberNEMO is therefore characterized by a shift from reactive performance observation to proactive, AI-driven security validation. By enriching the data previously used only for network optimization, we have created a robust mechanism for enforcing Zero Trust principles by design. This evolutionary step ensures that CyberNEMO doesn’t just provide a high-performance network, but a verifiably secure and resilient foundation for the next generation of meta-operating systems.
Read More

The MITRE ATT&CK framework for attacks

Understanding the MITRE ATT&CK Framework

In the world of cybersecurity, defenders and hackers are locked in a constant game of cat and mouse. For a long time, defenders focused on who was attacking them (attribution). However, names and locations change. The MITRE ATT&CK® framework shifted the focus to something more permanent: how they attack. ATT&CK stands for Adversarial Tactics, Techniques, and Common Knowledge. Think of it as a comprehensive, living encyclopedia of “bad guy” behavior. It is a globally accessible knowledge base that tracks the specific actions cybercriminals take from the moment they start scouting a target to the moment they steal data or cause damage.

The Anatomy of an Attack

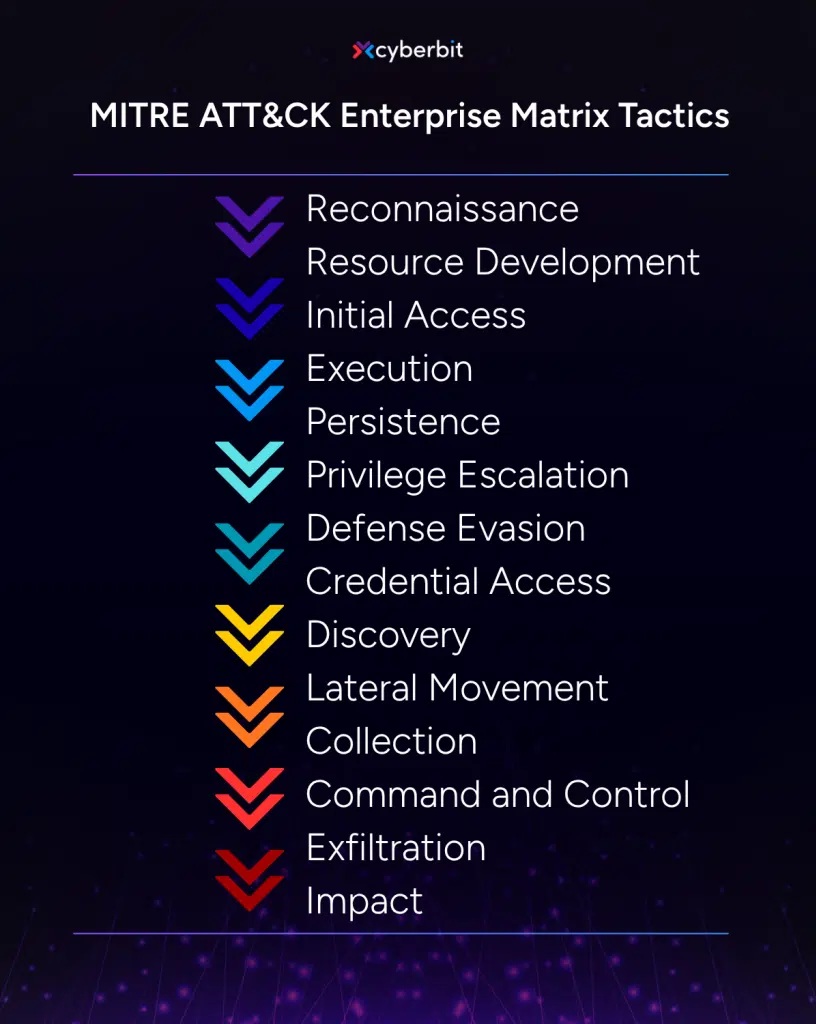
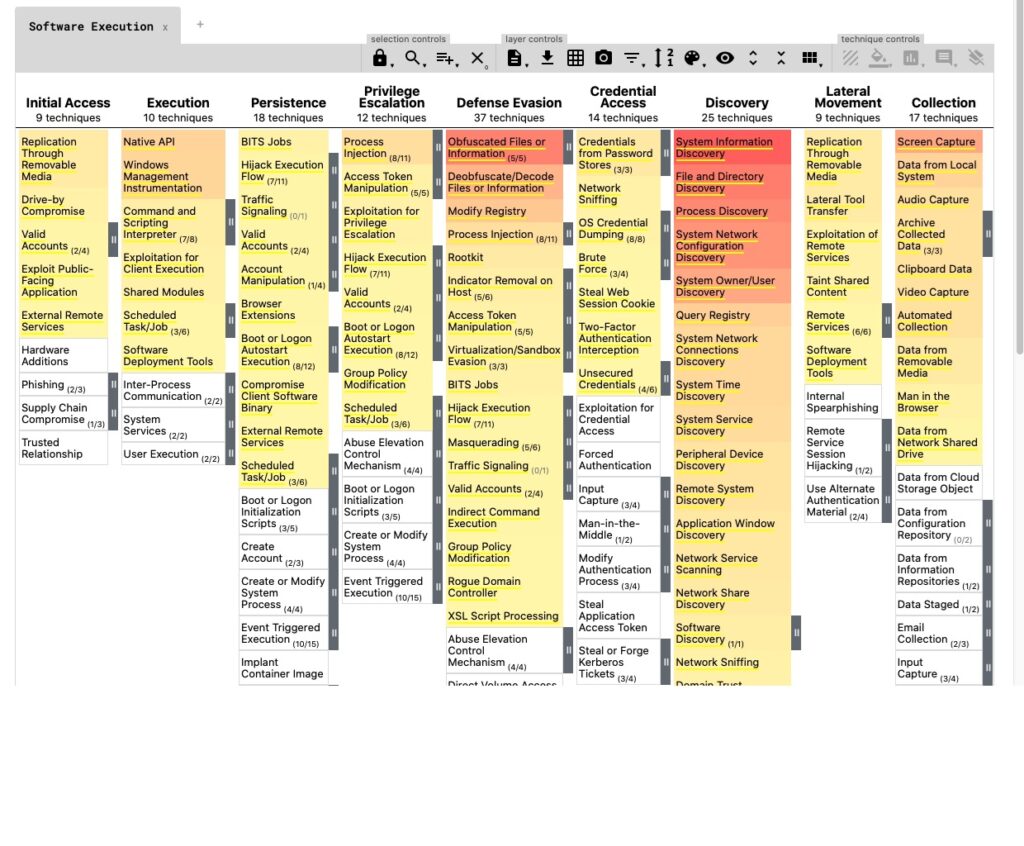
The framework is organized into a matrix that reads like a story of a digital break-in. It breaks down an attack into two main components: (a) Tactics (The “Why”): These are the attacker’s technical goals. For example, a tactic might be “Initial Access” (getting into the network) or “Exfiltration” (taking the data out). (b) Techniques (The “How”): these are the specific methods used to achieve a tactic. If the goal is “Initial Access,” the technique might be a “Phishing” email. By using this common language, security teams across different companies can share information instantly. If a bank in London discovers a new way hackers are bypassing passwords, they can label it with an ATT&CK ID (like T1078), and a hospital in New York will immediately know exactly what to look for.

Mitigations: Building the Shield

The framework isn’t just a list of threats; it’s a roadmap for defense. For every technique listed in the matrix, MITRE provides mitigations, i.e., specific actions organizations can take to prevent a technique from working.

TacticTechnique (Example)Mitigation (Defense action)
Initial AccessPhishingSecurity awareness training and email filtering.
PersistenceCreate AccountUse Multi-Factor Authentication (MFA) and monitor new user creation.
ExfiltrationTransfer Data to CloudBlock unauthorized cloud storage sites on the company network.

Why It Matters

While ATT&CK is a technical tool, its impact reaches everyone. When organizations use this framework, they move away from “guessing” what might happen and start “knowing” what to defend against. It allows companies to test their security systems against real-world scenarios, ensuring that your personal data and the services you rely on—like banking, healthcare, and power—are protected by more than just a firewall and a prayer. MITRE ATT&CK is a resource that has turned cybersecurity from a dark art into a measurable science by documenting the “playbook” of the adversary.

Read More

AI’s role in cyber risk assessment, monitoring and mitigation

AI: The New Digital Watchman

In the fast-moving world of the internet, new threats appear every second. Traditional security tools are like a library catalog—they work great for finding things we already know about, but they struggle with anything new. Artificial Intelligence (AI) has changed the game by acting less like a catalog and more like a highly trained digital watchman that never sleeps and learns as it goes. It contributes in monitoring, risk assessment and mitigation.

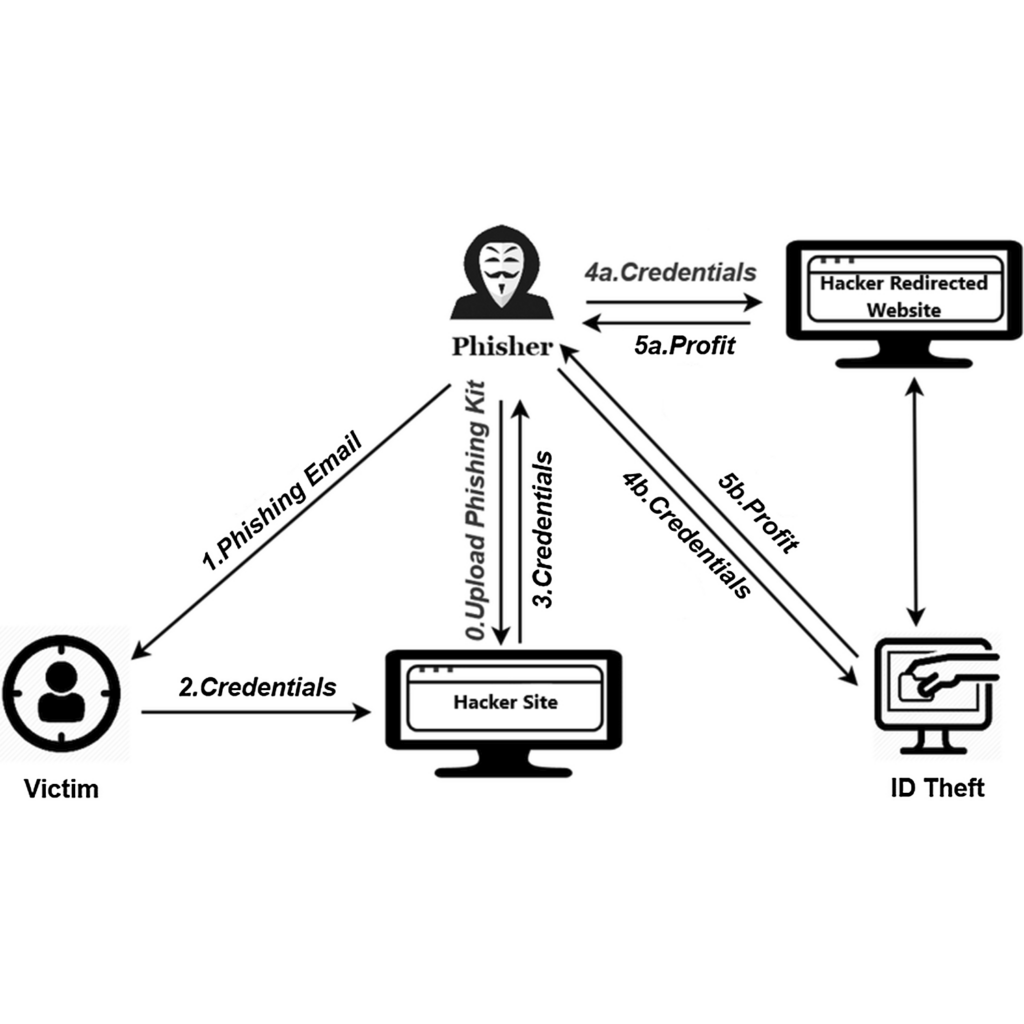
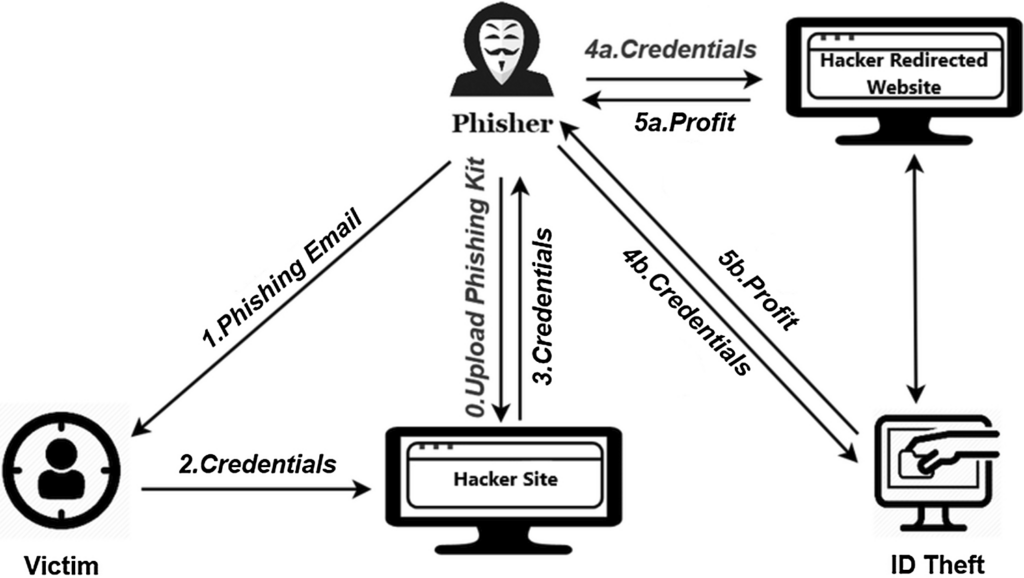
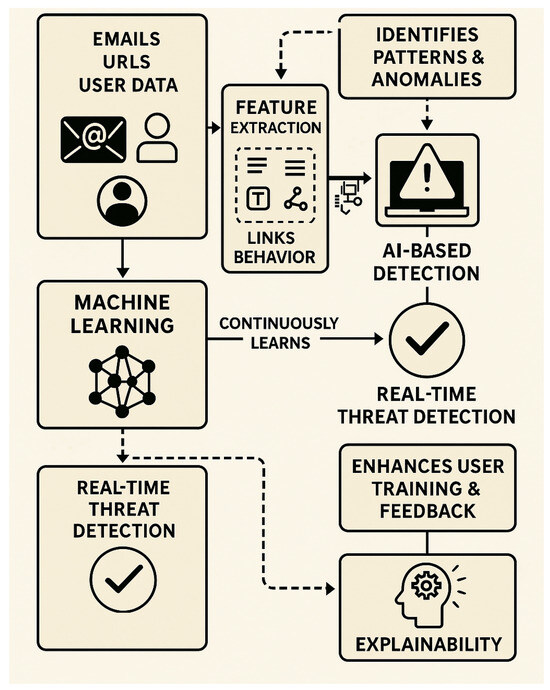
In monitoring it acts like the guard that never blinks. AI’s greatest strength is its ability to watch millions of events at once without getting tired. It can perform behavioral analysis and phishing detection. In behavioral analysis instead of just looking for “bad files,” AI looks for “bad behavior.” If an employee who usually only checks email suddenly starts downloading the entire company’s client list at 2:00 AM, the AI flags it as an anomaly. In phishing detectionAI can read the intent behind an email. It can spot the subtle signs of a scam—like a slightly misspelled link or a tone that is “too urgent”—and stop the email before it ever hits your inbox.

In risk assessment it can find the weak spots. Before an attack even happens, AI helps companies understand their “Cyber Risk”—basically, a score of how likely they are to be hacked. Often prioritizing is what matters. A large company might have thousands of software “vulnerabilities” (tiny bugs). AI can scan all of them and tell the security team, “These three are the most dangerous because hackers are currently using them to attack other companies.”. It can also support simulating attacks. AI can run “digital drills,” pretending to be a hacker to find paths through a network that a human might never think to check.

Finally, in mitigation, it can act at machine speed. When an attack happens, every second counts. AI allows a company to respond at “machine speed” rather than waiting for a human to wake up and read an alert. It can contribute in automated containment. If AI detects a virus spreading on one laptop, it can instantly “quarantine” that device, cutting its connection to the rest of the office so the virus can’t jump to other computers. Moreover, it can provide smart recommendations. If a threat is detected, AI can provide a “playbook” for the human staff, saying: “I’ve blocked the suspicious IP address. I recommend you reset these three user passwords and check this specific server for damage.”

While AI is fast, it isn’t perfect. It can sometimes mistake a legitimate heavy workload for an attack (a “false positive”). This is why the best cybersecurity is based on the human-AI partnership and uses a “Human-in-the-loop” approach. The AI handles the “heavy lifting” by filtering out 99% of the noise, allowing human experts to focus their energy on the most complex and dangerous 1% of threats.

Compared to traditional methods for security, AI-powered security offers many advantages. Instead of looking for known signatures (like finderprints) it looks for unknown patterns that may indicate suspicious behovior. Instead of requiring manual updates to stay current, it learns and adapts to new threats automatically. Moreover, it does not become overwhelmed by too much data; instead, it gets better the more data is processes.

AI has turned cybersecurity from a game of “catch-up” into a proactive defense, allowing us to predict and stop threats before they can do real damage.

Read More

Why Sockets Matter in Kubernetes: Beyond the Abstraction

In a standard Kubernetes (K8s) deployment, the sheer level of abstraction is a double-edged sword. While it simplifies orchestration, it often obscures the granular reality of network traffic. For the CyberNEMO project, specifically within WP2, we move past these high-level views to focus on the network socket. Why? Because sockets represent the “ground truth” of connectivity. In a distributed meta-OS, understanding the real-time state of point-to-point communication is the only way to ensure Cybersecurity and Privacy by Design.

Capturing the “Ground Truth” with White Shark

Traditional Kubernetes monitoring often looks at service-level averages, which can mask micro-bursts of latency or intermittent failures. By monitoring at the socket level, our White Shark probe can collect raw, high-fidelity data—including latency, throughput, and jitter—directly from the source. This allows us to see exactly how data moves between specific pods, bypassing the “fog” of virtualized overlays. This level of precision is essential for building a verifiable data plane, ensuring that every packet follows its intended path without manipulation.

Building a Stronger Zero Trust Foundation

Ultimately, focusing on sockets supports the Zero Trust principle of “explicit verification”. In CyberNEMO, we don’t just trust that a connection is secure because it’s inside the cluster. Instead, we use socket-based telemetry to constantly validate that communication patterns match the intended security policies.

Read More

The use of Explainable AI methods for monitoring assets, detecting cyberattacks, and suggesting mitigation actions

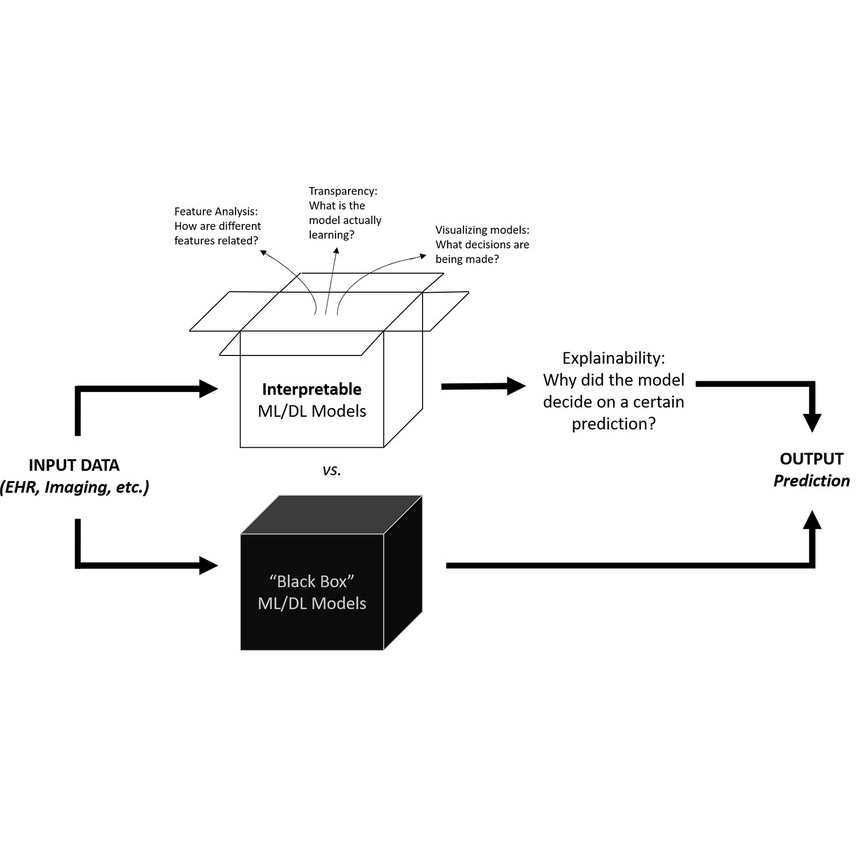
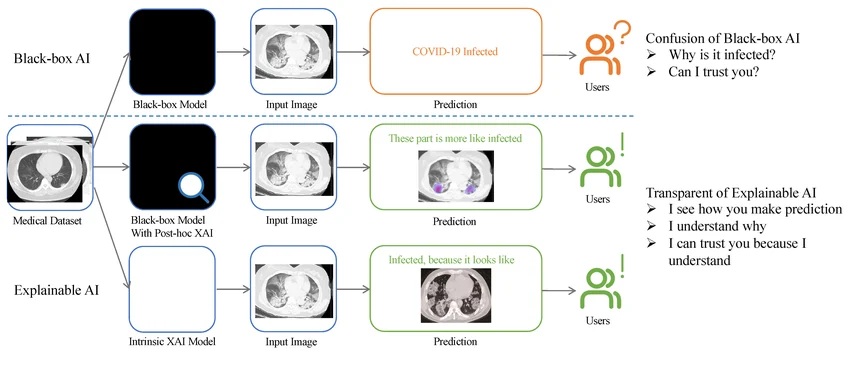
As cyberattacks become more frequent and complex, organizations are turning to Artificial Intelligence (AI) to defend their digital assets. Standard AI is incredibly fast at spotting patterns, but it often works like a “black box”—it might tell a security team, “This file is a virus,” or “there is a cyberattack going on from this IP addresss” without ever explaining why. For a security professional, a simple “Yes” or “No” isn’t enough. If the AI is wrong, it could block an important company document or block services that the company provides; if it’s right, the team still needs to know how the attacker got in to stop it from happening again. This is where Explainable AI (XAI) comes in.

What is Explainable AI (XAI)?

XAI is a set of tools and methods designed to make the “internal thought process” of an AI understandable to humans. In cybersecurity, XAI doesn’t just detect a threat; it provides a rational justification for its decision.

For monitoring assets and detecting attack instead of just monitoring for “bad” things, XAI helps security teams understand what “normal” looks like. If the AI flags a login attempt as suspicious, XAI can point to specific reasons: “The user is logging in from a new country” or “This account is suddenly accessing 2,000 files it never touched before.” XAI can generate maps or charts showing exactly where a network’s behavior deviated from the norm, helping humans spot the “smoking gun” quickly.

For suggesting mitigations XAI doesn’t just sound the alarm; it helps build the shield. By explaining the nature of the attack, it can suggest the best way to stop it.If the AI explains: “This is a Brute Force attack targeting the HR database,” the suggested action is clear: “Temporarily lock the targeted accounts and require a password reset.”

The Importance of the “User-in-the-Loop”

The most critical part of XAI is that it keeps a human—the User-in-the-Loop—at the center of the decision. Cybersecurity is high-stakes; a mistake could shut down a hospital’s network or a city’s power grid. XAI increases trust, facilitates collaboration and provides accountability.

  • Trust and Validation: When an AI can explain itself, a human expert can quickly verify if the alert is a real threat or a “false positive” (a mistake).
  • Collaboration: Humans bring “common sense” and context that AI lacks. For example, the AI might flag a large data transfer as an attack, but a human knows it’s just the annual company backup. XAI allows the human to see the AI’s logic, agree or disagree, and teach the system to be better next time.
  • Accountability: If something goes wrong, XAI provides a clear “paper trail” showing why a certain decision was made, which is essential for legal and safety audits.

The main differences between standard AI and explainable AI (XAI) are the following. In terms of output standard AI could mention that “High Risk is detected” but explainable AI would say “High Risk: Unusual data flow to an unknown IP is detected.” The human role is highly elevated in XAI from blindly trust or ignore the human to review evidence and take informed action. In addition, the learning process becomes stronger because instead of AI algorithms learning alone the human can provide feedback to refine the AI algorithms.

XAI transforms AI from a mysterious oracle into a transparent partner, ensuring that while the computer does the “heavy lifting” of data analysis, the human stays in control of the final defense strategy.

Read More

CyberNEMO SAAM: Building a Pan-European Cyber Shield for Critical Infrastructure

CyberNEMO SAAM is a pan-European Knowledge Sharing, risk Assessment, threat Analysis and incidents Mitigation collaborative platform designed to protect Critical Infrastructures (CIs) across Europe. Operating as the federated CTI exchange backbone of the broader CyberNEMO platform, SAAM serves as a pan-European CTI hub that collects, analysis, enriches, and distributes cybersecurity intelligence among interconnected infrastructure operators, national and cross-border cybersecurity authorities and communities. By centralising cyber threat data from diverse CI sectors including energy, transport, healthcare, and finance and structuring it around the widely adopted STIX 2.1 standard, SAAM creates a common operational picture that no single organisation could achieve on its own.

Modern cyber threats do not respect sector or national boundaries. A sophisticated attack on an energy grid can swiftly ripple into transport management systems or hospital networks, creating cascading failures that isolated, manually-processed intelligence cannot prevent. SAAM addresses this gap by positioning itself as the central nervous system of European CI cybersecurity, automatically correlating cross-sector incident patterns, attributing threats to known actors, and generating timely advisories for eligible partners. Governed by the most appropriate authority within the CyberNEMO ecosystem, and fully aligned with NIS2 compliance obligations, SAAM represents a significant step forward in building the collective resilience that Europe’s critical infrastructure communities urgently need.

SAAM delivers four tightly integrated capabilities. Cross-CI Knowledge Sharing enables the seamless exchange of CTI data across sector boundaries and national borders through secure Trusted Circles at Sectoral, National, Cross-Border, and Pan-European level utilizing interoperable standards such as STIX v2.1, TAXII 2.1 and Traffic Light Protocol (TLP) for controlled dissemination. SAAM’s Systemic Risk Analysis Engine applies automated analysis over incoming cyberthreat reports to score, correlate, and contextualise vulnerabilities and attacks. In addiiton, SRAE analysis contributes to the identification of coordinated attacks taking into account potential cascading effects. This contributes to SAAM’s enhanced State Awareness which gives operators and authorities a real-time, holistic view of the threat landscape across interconnected CI domains. Finally, SAAM’s Incident Mitigation translates enriched intelligence into actionable guidance, enabling CSIRTs and CI owners to coordinate responses swiftly and effectively before threats cascade across sectors.

Read More

CyberNEMO Exploitation Strategy overview

Europe’s cybersecurity landscape is under mounting pressure. The EU cybersecurity market, already valued at approximately €30 billion in 2023, is growing at a compound annual rate of 9–11%, driven by an escalating threat environment, accelerating digital transformation, and tightening regulation under frameworks such as NIS2, the Cyber Resilience Act, and the AI Act. Ransomware attacks targeting critical infrastructure are rising by over 25% annually, while nation-state actors, supply-chain compromises, and the convergence of IT and Operational Technology (OT) networks continue to expand the attack surface. Across key verticals such as energy, healthcare, cloud, edge computing, IoT, and data management. CyberNEMO’s market analysis reveals a consistent pattern suggesting that demand is surging, solutions are fragmenting, and the gap between security investment and actual resilience is widening. Particularly underserved are small and medium enterprises, operators of critical infrastructure burdened by legacy systems, and the growing edge computing segment, where cybersecurity spending is already struggling to keep pace with infrastructure deployment.

CyberNEMO’s competitive advantage rests on five interconnected pillars. As an EU-funded initiative built on EU-sovereign infrastructure, it is fully aligned with the EU Cybersecurity Strategy, directly advancing Europe’s goal of strategic digital autonomy. This is reinforced by a unique public-private partnership model that grants privileged access to CERT and regulatory bodies alongside established relationships with critical infrastructure operators. The platform’s credibility is further substantiated by its validation across six diverse pilot sectors, providing concrete cross-domain applicability evidence that spans energy, healthcare, media, agrifood, logistics, and fintech. By anchoring its open-source core within the Eclipse Foundation, CyberNEMO fosters community-driven development that actively reduces vendor lock-in, encouraging broad adoption while preserving transparency and trust. Finally, the platform has been designed from the outset with regulatory foresight, embedding compliance with NIS2, the Critical Entities Resilience Directive (CER), the AI Act, and the Cyber Resilience Act directly into its architecture — positioning it as a ready-made solution for organisations navigating Europe’s increasingly demanding cybersecurity regulatory landscape.

CyberNEMO, delivers an end-to-end, zero-trust cybersecurity framework purpose-built for the Cloud-Edge-IoT-Data computing continuum. Following IEEE 42010 methodology, stakeholder concerns were systematically mapped to architectural viewpoints. Each viewpoint addresses specific concerns through defined architectural perspectives, conventions, and models covering viewpoints such as development, process, user, business and security ones. CyberNEMO has identified twelve Key Exploitable Results (KERs) that offer capabilities ranging from real-time AI-driven anomaly detection and explainable AI (XAI) to interoperable and standardized threat intelligence sharing, micro-services auditing and certification, and federated risk assessment across borders.

CyberNEMO’s multi-dimensional approach which combines financial self-sufficiency through subscription services, institutional permanence through Eclipse Foundation governance, regulatory foresight and community network effects through open-source engagement aims to position it to deliver lasting value to European Critical Infrastructure and citizens well beyond the project’s formal completion.

Read More

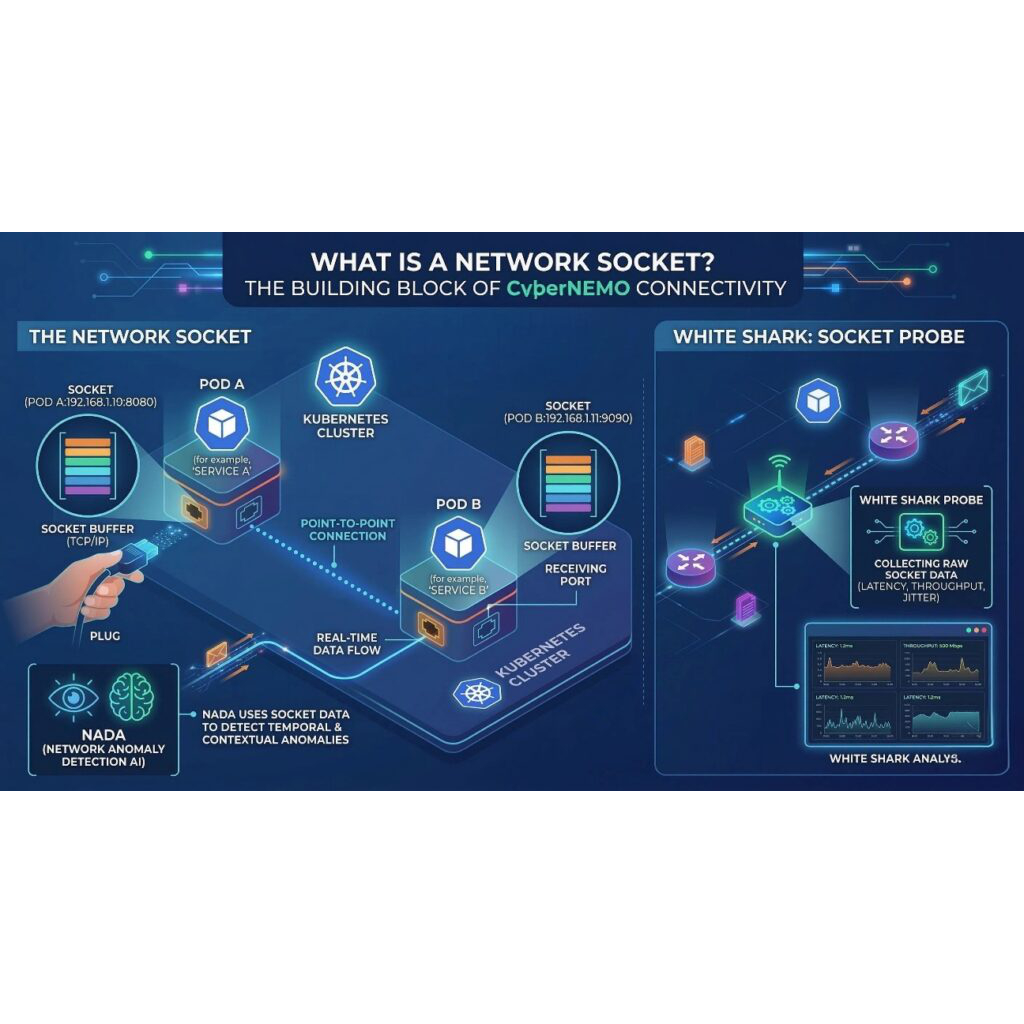
What is a Network Socket? The Building Block of CyberNEMO Connectivity

In the complex architecture of the CyberNEMO meta-Operating System, ensuring secure and reliable communication across the computing continuum is paramount. While high-level security frameworks like Zero Trust Network Access (ZTNA) provide the overarching strategy, the actual heavy lifting of data exchange happens at a much more fundamental level: the network socket.

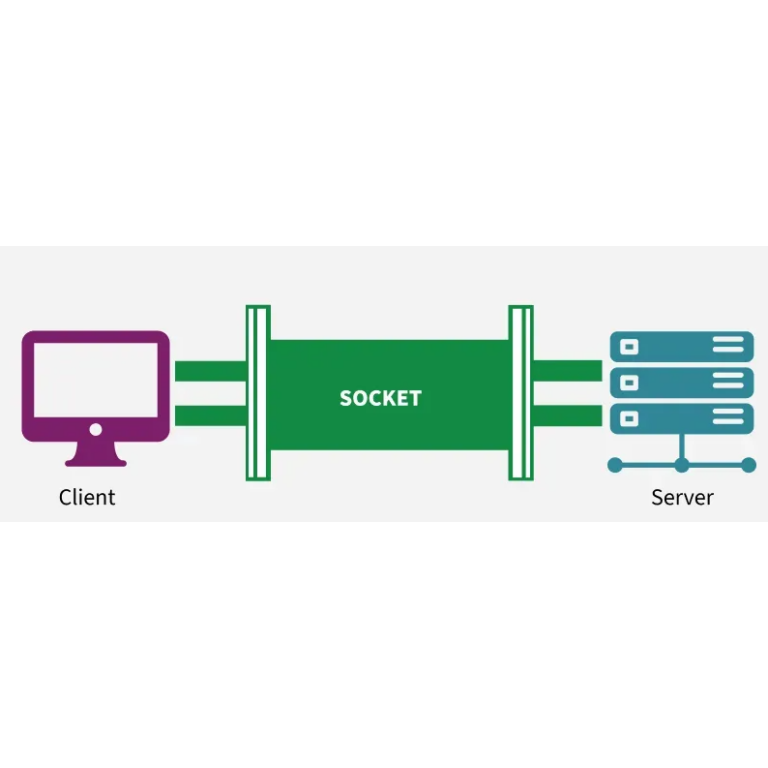
A network socket is essentially an internal endpoint for sending or receiving data at a single node in a computer network. Think of it as a virtual “plug” that allows two different processes—whether they are on the same machine or across the world—to talk to each other. In a Kubernetes (K8s) environment, which serves as the foundation for CyberNEMO’s deployment, sockets are the critical bridges between containerized microservices. They enable the point-to-point communication necessary for workloads to function as a unified system.

Why Sockets Matter for Network Measurement

Within the WP2 (Work Package 2), the focus is on “Cybersecurity and Privacy by Design”. To achieve this, we cannot rely on surface-level metrics. We need to measure real communication at the socket level. This is where components like White Shark come into play.

Originally developed for the NEMO project, White Shark is a specialized network probe designed to collect and retrieve high-fidelity network data. By tapping into socket communication, White Shark can measure point-to-point metrics—such as latency and throughput—directly between two endpoints. This provides a level of precision that traditional network monitors often miss, as it captures the actual data flow as seen by the applications themselves, rather than just the underlying infrastructure.

From Raw Data to Intelligence: The Role of NADA

Capturing socket-level data is only half the battle; the next step is making sense of it. In CyberNEMO, this data is fed into the Network Anomaly Detection AI (NADA). NADA’s purpose is to identify temporal and contextual anomalies—suspicious patterns in the network traffic that could indicate a security breach.

Read More

Advancing Smart Healthcare and Cyber-Resilient Infrastructures

XGL (Xgility) is an innovative solutions provider and research-oriented IT company headquartered in Dublin, Ireland. Bringing together a highly skilled and diverse team of researchers, consultants, and IT specialists, XGL delivers a comprehensive range of services and solutions tailored to the needs of both industry and research partners. The company is distinguished by its agility, technical expertise, and forward-looking approach to technology adoption.

XGL’s core competencies span software development, IT outsourcing, AI-driven decision support systems, cybersecurity expertise, IT consulting, training, and advanced data and document management. Building on its innovation-driven approach, the company is also exploring emerging technologies such as virtual agents and large language models (LLMs) to enhance digital services, automation, and human–machine collaboration. By combining cutting-edge research with hands-on experience in the deployment and management of complex IT solutions, XGL supports organizations in their digital transformation journeys. With a strong emphasis on reliability, scalability, and adaptability, XGL has established itself as a trusted partner capable of addressing diverse technological and business challenges.

Beyond its service portfolio, XGL actively participates in research and innovation through EU-funded projects, where it contributes to the advancement of IT infrastructures, interoperability, and digital resilience. Its longstanding involvement in European research initiatives highlights the company’s ability to bridge the gap between academic innovation and industrial application, translating research outcomes into market-ready solutions through a strong commitment to research-to-market dissemination.

Within the CyberNEMO project, XGL plays a pivotal role by leading Task 5.1: Open Data Management Plan & Trials Set-up and Task 5.4: Smart Healthcare Critical Infrastructures Validation, where it provides guidelines for data management in CyberNEMO and supports the MUP pilot with technical expertise. In addition, XGL contributes to Task 3.2: Intrusion Prevention/Detection/Mitigation DSS (IPDM-DSS) and Task 3.4: Privacy Protection Enforcement (PPE). The company also leads the development of a semantically enhanced Countermeasures Repository, designed to identify and match countermeasures against emerging and existing critical infrastructure threats.

Through its expertise in cybersecurity, AI-driven solutions, and emerging virtual agent technologies, XGL reinforces the collaborative and interdisciplinary character of CyberNEMO. The company remains dedicated to driving innovation, enabling digital transformation, and delivering high-quality IT solutions that create long-term value for stakeholders across both research and industry.

Read More

Mapping Cyber Vulnerabilities to MITRE ATT&CK for Critical Infrastructure Threat Detection

How CyberNEMO is bridging the gap between risk visibility and intelligent response

In today’s hyperconnected world, Europe’s critical infrastructures (CIs) — energy, transport, healthcare, and manufacturing — form the backbone of our digital society. Yet these same systems are among the most vulnerable targets. 

From ransomware attacks that paralyse hospitals to supply chain breaches rippling through industrial control systems, one reality stands out: we cannot defend what we cannot understand. 

Why Vulnerability Mapping Matters

Traditional vulnerability scanning stops at detection — identifying weak points without explaining how they might be exploited. But true cyber resilience requires context. 

By mapping vulnerabilities to the MITRE ATT&CK framework — the global reference for adversarial tactics, techniques, and procedures (TTPs) — defenders can see how attackers think and operate. Each vulnerability becomes a narrative of potential attack paths, not just a static CVE entry. 

By correlating technical weaknesses (CVE/CVSS) with ATT&CK techniques, CI operators can: 

  • Prioritise what matters most — focusing on vulnerabilities exploited by active adversaries.
  • Enhance detection logic — linking vulnerabilities to ATT&CK techniques like privilege escalation, lateral movement, or data exfiltration.
  • Enable AI-driven threat prediction — modelling how small weaknesses could evolve into full-scale attack chains.

Embedding AI Closer to the Threat Surface

CyberNEMO’s approach brings AI intelligence directly to the edge, transforming how vulnerabilities are monitored and analysed in distributed systems. 

By embedding AI in IoT gateways and edge devices, threat detection becomes continuous, adaptive, and privacy-preserving. These local models evolve with each new observed attack, strengthening defences autonomously and enhancing cross-domain resilience. 

This shift — from centralised analysis to distributed intelligence — is key to protecting the complex, hybrid environments that define modern critical infrastructure. 

From Zero Trust to Full-Stack Protection

As CI systems increasingly span IoT–edge–cloud architectures, the attack surface expands. MITRE ATT&CK provides a shared taxonomy for identifying and analysing threats across layers — whether it’s an IoT device communicating with a suspicious domain (ATT&CK T1071) or an insider escalating privileges (T1068). 

When integrated with Zero Trust principles, ATT&CK mapping enables defenders to: 

  • Dynamically verify every entity and data flow.
  • Feed contextual intelligence into security enforcement engines.
  • Apply risk-based adaptive access control, tightening security automatically when certain attack techniques are detected.

Together, these approaches move organisations from reactive defence to proactive, intelligent protection. 

Collaboration and Knowledge Sharing

Mapping vulnerabilities to MITRE ATT&CK isn’t just a technical process — it’s a collaborative intelligence effort. 

CyberNEMO is shaping a distributed European sharing platform that empowers CI operators, CERTs, and CSIRTs to:

  • Exchange ATT&CK-aligned threat data in real time.
  • Maintain interoperability across domains and sectors.
  • Strengthen Europe’s collective cyber resilience.

By aligning on a common threat language, Europe’s CI defenders can respond faster and smarter — together. 

Building a Culture of Cyber Sustainability

Ultimately, mapping vulnerabilities to MITRE ATT&CK helps organisations do more than just patch; it helps them learn, adapt, and evolve. 

By connecting the technical (AI, Zero Trust, machine learning pipelines) with the human (awareness, collaboration, and shared intelligence), CyberNEMO fosters a culture of cybersecurity for sustainability — one that endures and grows stronger over time. 

The Path Forward

CyberNEMO’s work on vulnerability-to-ATT&CK mapping marks a crucial step toward AI-empowered, collaborative cyber defence across Europe’s critical infrastructure. 

It bridges the gap between visibility and action, turning fragmented vulnerability data into a living intelligence fabric that evolves with every threat. 

Because in this new era of cyber-physical convergence, context is the ultimate defence.

Read More