Cyber risk rarely stops at the boundary of a system
Traditional cybersecurity assessments often begin with a product, application or infrastructure component. The objective is to identify vulnerabilities, understand relevant threats and determine whether available controls reduce the risk to an acceptable level.
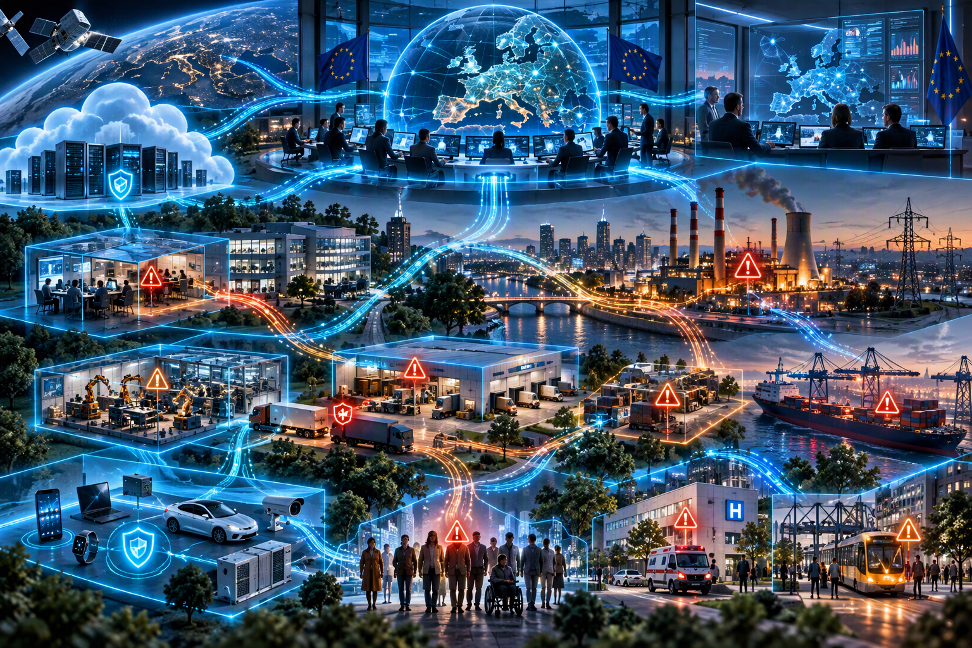
That remains essential, but it is no longer sufficient. Modern critical infrastructures depend on interconnected software, cloud services, edge platforms, operational technology, data providers and external suppliers. A vulnerability originating in one product may affect an organisation’s operations, spread through a supply chain and ultimately influence services delivered to society.
A major development in CyberNEMO D1.3 is the introduction of a structured hierarchy connecting these different risk perspectives.
Three connected views of risk
Product and system risk concerns an individual product, service or system of systems. The assessment examines how vulnerabilities, misconfigurations, design weaknesses or foreseeable misuse could affect intended operation. Its result is an evidence-based description of how a product could contribute to broader operational consequences.
Product-level assessments then become inputs to organisational risk management. At this level, organisations determine what a technical failure means for business processes, service continuity, compliance obligations, financial exposure and operational resilience. Multiple product risks may need to be combined because organisational impact rarely depends on one component alone.
The broadest level concerns value-chain and societal risk. Critical infrastructures rely on shared technologies and services, so a cyber incident in one organisation can trigger disruption elsewhere. Organisational risk postures from federated nodes can be correlated against cross-sector dependencies to detect coordinated threats, cascading effects and supply-chain exposure.
From isolated risks to cascading consequences
A technical vulnerability may initially appear limited to a single asset. Its significance changes when dependencies are considered. A compromised service may affect the availability of a business function, the integrity of information exchanged with partners, the operation of connected infrastructures or another organisation’s ability to deliver an essential service.
The key question therefore changes from how severe a vulnerability is to where the resulting disruption can propagate. This dependency-aware perspective reveals risks that cannot be understood by analysing individual components in isolation.
Why aggregation is difficult
Risk aggregation is not simply the addition of multiple scores. Product assessments may use different scales, assumptions, data sources and levels of confidence. Some describe technical severity; others measure business impact or operational disruption. Combining them without preserving this context may produce a misleading organisational view.
A defensible process must retain the original evidence, assumptions, uncertainty and data-quality information, dependencies among assets and organisations, the rationale for escalation and the controls operating at different levels. Traceability is therefore a prerequisite for moving from product risk to organisational and value-chain risk.
Federated awareness without centralising everything
Cross-organisational risk management requires useful intelligence to be shared without unnecessarily exposing sensitive operational information. In a federated model, each organisation can maintain control of local data and decisions while contributing selected information to a collaborative layer.
The shared layer can identify related attacks, repeated vulnerabilities, shared dependencies and potential cascading consequences that would remain invisible to an isolated participant. The objective is not central control of every local decision, but a common situational picture built from distributed evidence.
Risk management across the lifecycle
D1.3 explicitly connects product risk management with system use, DevSecOps, incident response, certification, governance and pre-market and post-market monitoring. Risk begins before deployment and continues after a system enters operation.
Design decisions, third-party components, deployment conditions, operational changes and newly discovered vulnerabilities may all change the risk posture. Assessment must therefore accompany conception, design, development, verification, deployment, operation, continuous validation, re-evaluation and retirement.
The key lesson
Cybersecurity risk management can no longer stop at the product boundary. Product risks must be translated into organisational consequences and examined against the dependencies connecting suppliers, operators and critical services.
TAKEAWAY A mature cyber-risk model preserves traceability while moving from component-level evidence to organisational decisions and cross-sector situational awareness.
Editorial basis: CyberNEMO D1.3. Public-facing version with no sensitive operational details.